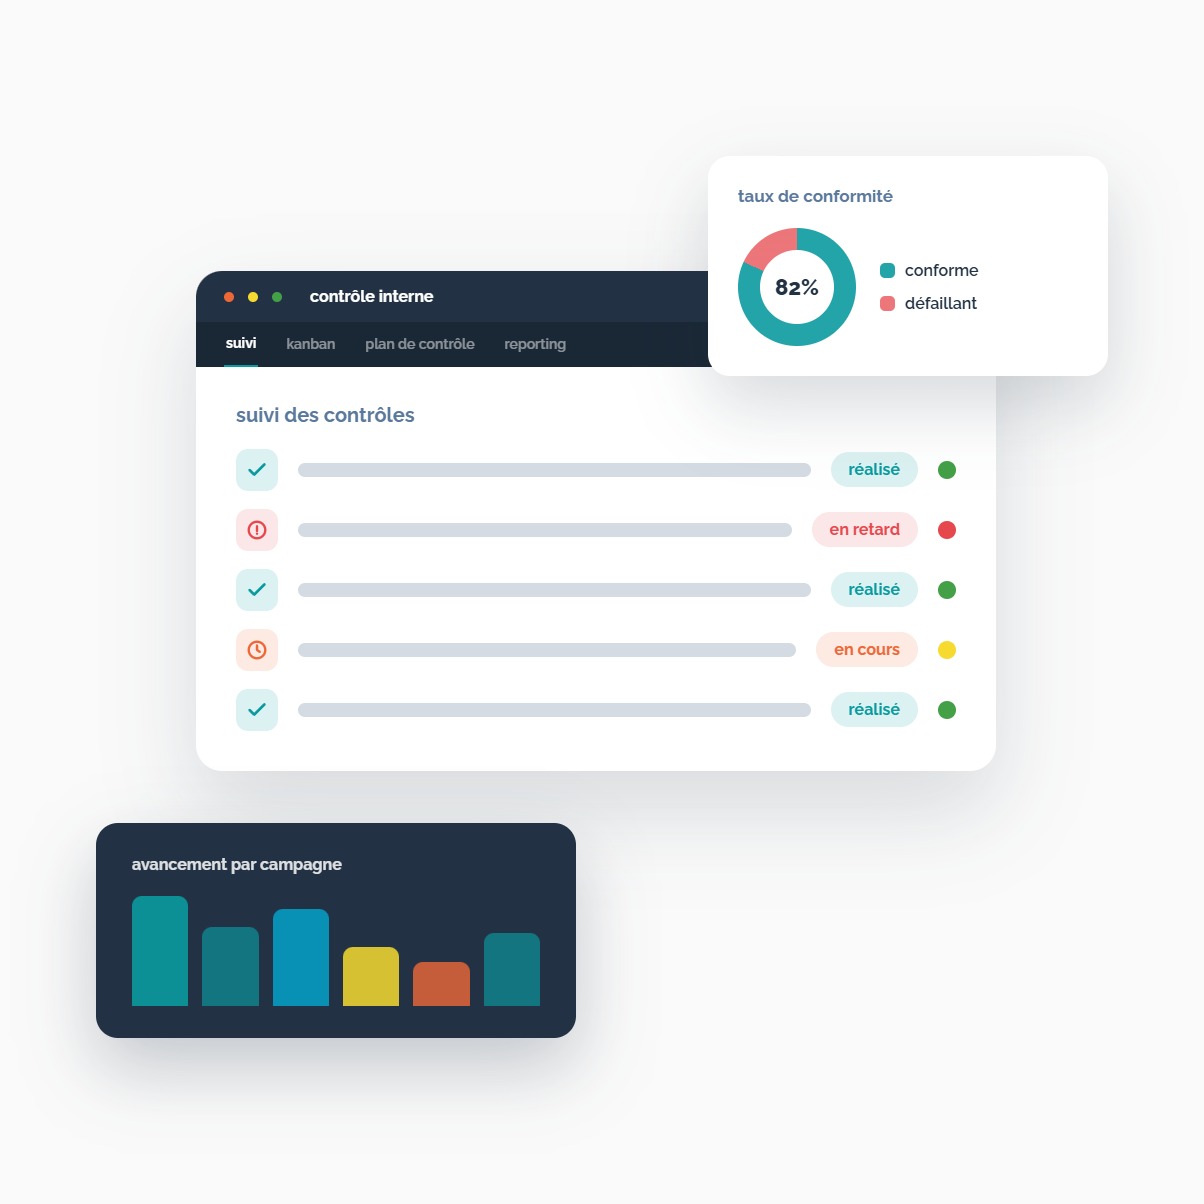
Our internal control software enables organisations to plan, carry out, document, and monitor their internal controls in a centralised repository.
It structures campaigns, assigns owners, centralises evidence, consolidates results, and makes it easier to demonstrate the effectiveness of the programme.
Each entity manages its controls in its own files. Repositories diverge, evidence stays local, and group-wide consolidation takes too much time.
Our software centralises campaigns across all entities. Each local owner follows the group repository, carries out their controls, documents the results, and attaches evidence within the same tool.
Management gets a consolidated, real-time view, with no manual aggregation or scattered email reminders.
You need to manage recurring control campaigns, but instructions, deadlines, and expected evidence are scattered across departments.
Our software structures campaigns, guides each owner step by step, centralises evidence, and automates reminders based on set deadlines.
Your programme is formalised, traceable, and ready to be presented without last-minute reconstruction.
You need to demonstrate the effectiveness of your permanent controls to regulators such as the AFA, ACPR, AMF, etc., or to your auditors. Evidence is scattered, and files need to be reconstructed before every review.
Our software centralises control results, related evidence, comments, and corrective actions in a structured, exportable file.
You get a complete control file, available at any time for your regulators, auditors, or internal committees.

Centralize and qualify your libraries of processes, risks, and controls in a single, structured repository aligned with your organization.
Link elements together to benefit from a 360° view of your framework.
Not sure where to start? Use our pre-configured libraries to get started quickly.

Each manager performs their controls, documents the results, adds comments, and attaches evidence directly in the tool.
The history remains traceable, without any file exchanges.

Track campaign progress, overdue controls, results, areas of weakness, and associated action plans.
Export reports ready for management, auditors, or regulatory authorities.
Intuitive and fully customisable, it helps you effectively identify and analyse the risks your organisation is exposed to.
Processes, risks, controls, entities, and evaluation criteria are centralised in a shared repository. Each entity works from the same base, with its own responsibilities.
Each control is documented with its evidence, comments, statuses, and approvals. You get traceability you can rely on for your audits, committees, or external controls.
Our software works on its own. If you want a complete GRC view, it can be connected to risk mapping, internal audit, action plans, and incident management in our GRC solution.
Manage several control frameworks in the same tool: Sapin 2, ACPR, AMF, NIS2, DORA, or internal frameworks. Each framework keeps its own criteria, controls, and requirement levels.
Show us your programme. We’ll present the tool suited to your context, then discuss your project to define the most appropriate support.

Our Internal Control software can be used on its own or integrated into our GRC solution to link your controls to your risks, audits, and action plans. Coverage possible depending on the frameworks activated: Sapin 2, NIS2, DORA, ESG, ACPR, AMF, AI Act.
Deploy only your internal control process. You address a specific need, without taking on an entire programme.
Connect your internal audit software to the 4 modules of the GRC solution for a consolidated view, shared data, and a single file ready for any audit.
Three engagement levels based on your GRC maturity and the complexity of your organisation.
Internal control software makes it possible to plan, carry out, document, and monitor an organisation’s permanent controls in a centralised repository. It structures campaigns, assigns owners, centralises evidence, and produces the reports needed to demonstrate that the programme is in place.
Dedicated software replaces scattered files with a shared repository. Campaigns are planned, owners are notified, evidence is centralised, and results are consolidated automatically. Management, internal control teams, and auditors access an up-to-date view of the programme.
Several frameworks may require a structured internal control programme: Sapin 2, ACPR/AMF requirements, NIS2, DORA, ESG, or internal frameworks. Our software makes it possible to adapt control frameworks to the frameworks activated by your organisation.
Yes. Our software supports multi-entity organisations: each subsidiary, department, or site carries out its controls within its scope, while the central level has a consolidated view. Roles and permissions can be adapted between local teams and the central team.
With the Essential offer, deployment can take under a week with a pre-configured repository. With the Configurable offer, allow 3 weeks to 1 month to adapt the software to your repository, entities, and workflows. For a Made-to-measure project, the timeline is defined based on the scope.
Yes. Our Internal Control software can be deployed on its own. It can also be connected to our Risk Mapping, Internal Audit, and Action Plan software within our GRC solution if you want an integrated view of your programme.
Internal control software helps structure campaigns, centralise evidence, track results, and produce reports. It does not replace the quality of the controls carried out or the organisation’s decisions, but it greatly facilitates demonstrating and tracing the programme.