Our incident management software enables every employee to report an incident in a few clicks, then manage its processing until closure: qualification, successive reviews, remediation action plan, and automatic registry update.
Natively linked to your risk mapping and controls, it allows you to refine your scoring based on actual incidents.
Incident reporting relies on email or shared files. Employees lack a simple channel to report what they observe, and some incidents are never escalated.
Every employee reports an incident in a few clicks, directly within the tool. The module integrates with your GRC solution without burdening your existing processes.
You capture unforeseen events as they occur, without depending on individuals' willingness to send an email.
A reported incident doesn't always have a clear follow-up: who should review it, when is it closed without action, who decides if remediation is needed?
A dedicated manager handles the incident's processing, from qualification to closure, with a multi-level review workflow (N+1, then internal control correspondent) and the possibility of closing without action at each stage.
Each incident follows a defined and traceable workflow, with no gray areas regarding who needs to act or by when.
Once a corrective action is decided, its tracking often gets lost in a spreadsheet or email inbox, without formal validation of closure.
The remediation action plan associated with the report is managed by a dedicated person, with progress updates and a closure request submitted for validation before the incident is considered resolved.
No remediation closes without validation, and the incident register is automatically updated at each key step of the process.

Empower every employee to report an incident in just a few clicks without sending an email.
A short form guides the reporter: nature of the incident, entity and process involved, date, description, and attachments
The report is signed and recorded before being sent to the review workflow.

The dedicated manager ensures the incident is handled from qualification through to closure.
Incidents may be linked (or not) to your risks or your controls.
They manage the action plan associated with the incident, update its progress, and submit the closure request for validation by the internal control contact.

Linked incidents are displayed directly during risk assessment and control monitoring.
Refine the inherent scoring of your risks and the evaluation of your controls by taking reported incidents into account.

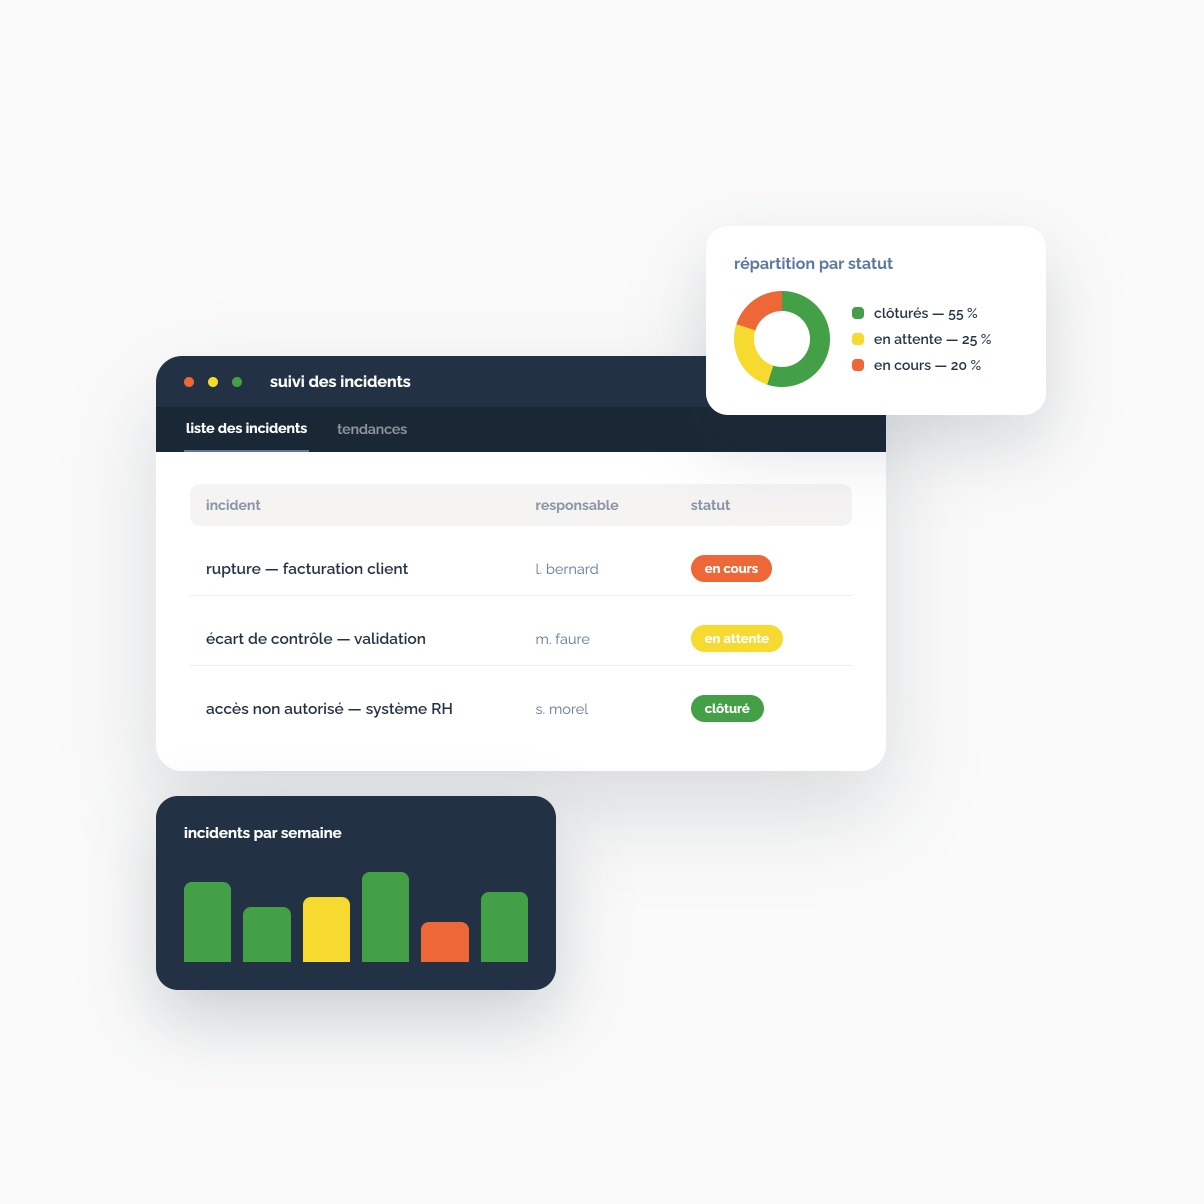
Manage and analyze reported incidents from a single interface: status, owner, and processing time for each.
Pending or overdue cases are automatically flagged, allowing for reminders to be sent before delays occur.
Observed trends inform the periodic review of the system.
Intuitive and fully customizable, it helps you effectively identify and analyze the risks your organization faces.
Classify your incidents by category (fraud, operational error, system/IT failure, information security, regulatory non-compliance, health-safety-environment...) and by severity level (low, medium, high, critical), using a library adjustable to your context.
The processing workflow (reporter, N+1, internal control correspondent, action plan manager) is configurable according to your organization, without development.
Incident management works on its own but integrates natively with risk assessment and control monitoring of our GRC solution: each incident can be linked, or not, to a risk or a control.
Every step of the review process, follow-up, and closure automatically updates the incident register, with a complete history accessible at any time.
Let us show you our system to discover the tool adapted to your context, discuss your project with us, and define the most suitable support.

The incident management software can be used independently. It can also integrate with our GRC solution to connect your incidents to your risk mapping, controls, and action plans.
Deploy only your incident management. You address a specific need without implementing an entire programme.
Connect your incident management software to the 4 modules of the GRC programme for a consolidated view, shared data, and a single file ready for any audit.
Three engagement levels based on your GRC maturity and organizational complexity.
Incident management software is a tool that allows every employee to report an undesirable event (fraud, breakdown, non-compliance, operational error…) and manage its processing until closure. It structures the qualification, review, remediation, and traceability of each reported incident.
An Excel file centralizes a list of incidents, without workflows or automatic traceability of decisions made. Incident management software structures the reporting, review, and remediation workflow, with statuses, notifications, and a registry automatically updated at each step.
No. An incident can be processed autonomously, without being linked to a risk or control. It can also be attached to an existing risk or control: in this case, it objectively informs the scoring of the risk or the evaluation of the control concerned.
The reporter submits their report, which is successively reviewed by their N+1 and then by the internal control correspondent. At each stage, the incident can be closed without action or forwarded to the next stage. If it requires remediation, an action plan manager oversees its processing until closure validated by the internal control correspondent.
Yes. The incident management software can be deployed standalone. It can then be linked to risk mapping, internal control, and action plans within the GRC Solution, to objectively inform your scoring based on actual incidents.
With the Essential offer, deployment can be done in less than a week thanks to the pre-configured standard review workflow. With the Configurable offer, it generally takes 3 weeks to adapt the workflow and incident categories to your organization.