Our third-party integrity assessment software enables organisations to centralise, qualify, and track the integrity of third parties as part of their anti-corruption programme.
It structures questionnaires, automates reminders, consolidates responses, records decisions, and makes it easy to produce a usable file in the event of an audit.
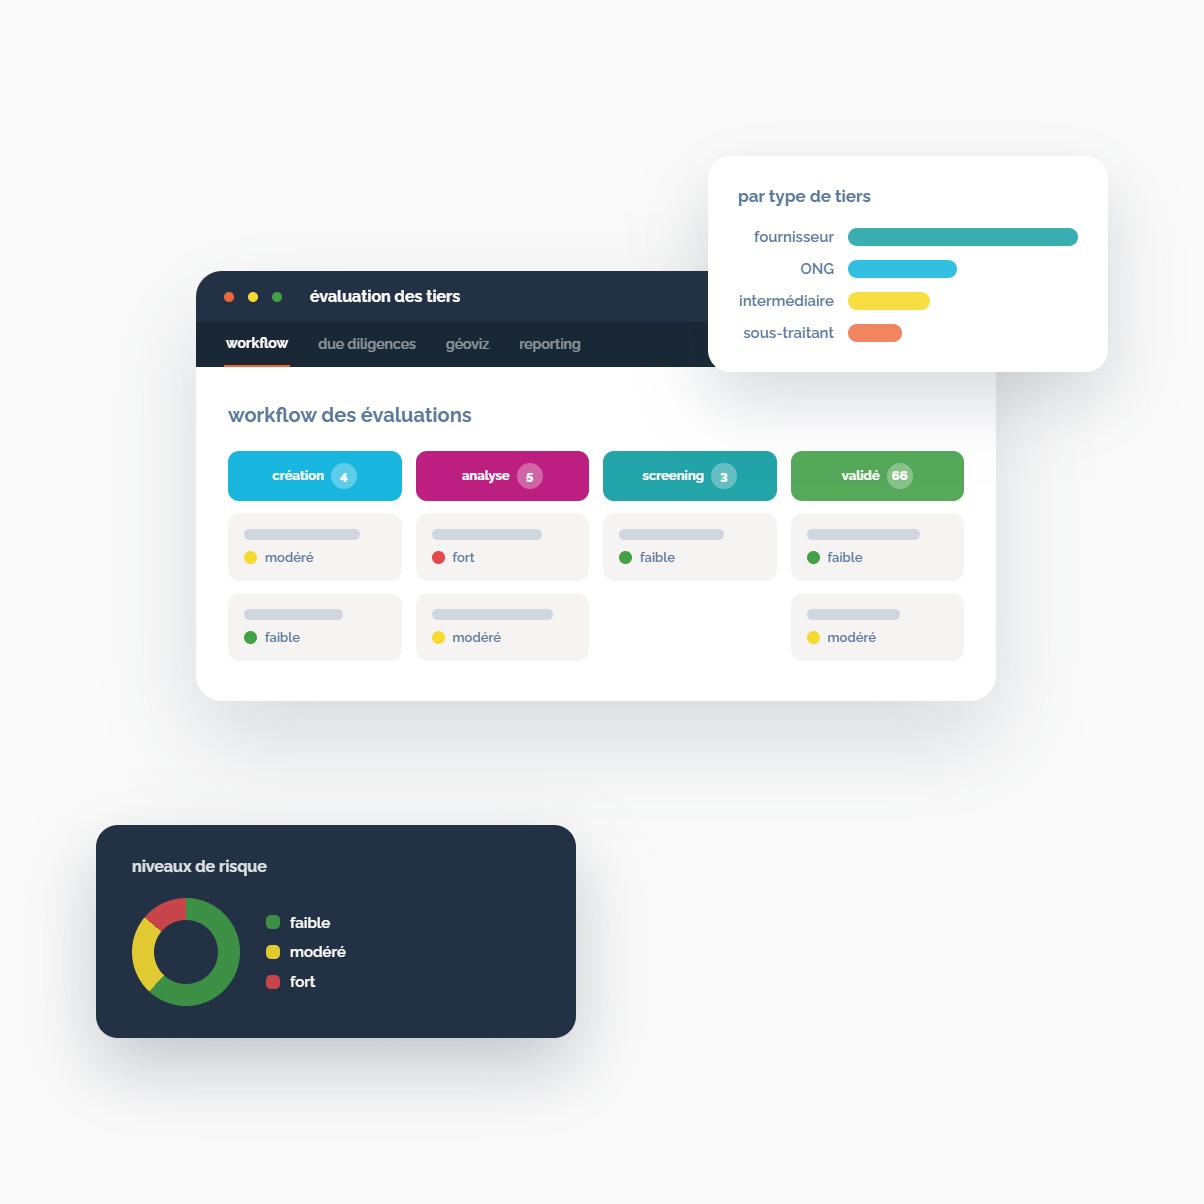
Each entity assesses its third parties using its own files, its own reminders, and sometimes its own criteria. Duplicates multiply, files are incomplete, and producing a group-level view remains difficult.
Our software centralises your third parties in a shared repository, limits duplicates, and enables you to pre-qualify their risk level according to your Sapin 2 criteria, your entities, and your relationship types.
Your teams reduce time spent on duplicates and consolidation. They focus on genuinely sensitive third parties.
Your assessment process exists, but it still relies on files, email exchanges, and scattered evidence. In the event of an audit, producing a clear and complete file takes too much time.
Our software structures third-party integrity assessment: centralisation, questionnaires, scoring, reminders, responses, decisions, and history. Every step is documented and exportable.
You have a structured, usable, and traceable assessment file, without last-minute reconstruction before an audit or inspection.
You have a large volume of third parties to assess. Manual reminders take too much time, response rates vary, and files are not always consistent.
Questionnaires are triggered according to risk level. Reminders are scheduled, responses centralised, and scoring applied consistently across the entire portfolio.
You structure assessment at scale, without multiplying manual follow-ups. Your teams focus on high-stakes files.

Centralize key information about your third parties: legal name, third-party type, relevant entity, identifiers, geographical area, business relationship, and risk level.
Deduplication limits redundant assessments.

Trigger questionnaires tailored to the third party’s risk level.
Reminders are scheduled, responses are centralized, and scoring is applied according to your evaluation rules.

With built-in artificial intelligence, the solution accelerates the collection and synthesis of third-party information to facilitate and secure decision-making.

A guided process orchestrates each step of due diligence and facilitates collaboration between teams. It ensures reliable decisions, guarantees traceability of actions, and reduces operational burden.
Intuitive and fully configurable, it helps you identify and analyse the risks your organisation is exposed to efficiently.
Our AI automatically collects information available on the web, in multiple languages, and produces a clear, sourced summary. Built on Mistral's French models and hosted in France, it reduces analysis time and helps you decide which third parties to investigate further.
A shared repository consolidates your third parties across all your entities. Deduplication limits redundant assessments and improves portfolio consistency.
Our software is designed to structure third-party integrity assessment as part of an anti-corruption programme. Questionnaires, criteria, and scoring grids can be adapted to your internal policy and risk levels.
Our software works on its own and connects to other Sapin 2 pillars to progressively build a more complete anti-corruption programme.
Show us your workflows. We’ll present the tool suited to your context, then discuss your project to define the most appropriate support.

Our Sapin 2 third-party assessment software can be used on its own or integrated into our Sapin 2 solution to link your actions to the other pillars of your anti-corruption programme.
Deploy only your third-party assessment, with its anti-corruption business content. You address a specific need, without taking on an entire programme.
Complete your third-party integrity assessment with the eight pillars of the programme for a consolidated view, shared data, and a single file ready for any audit.
Three engagement levels according to your GRC maturity and the complexity of your organisation.
Under Sapin 2, third-party assessment involves analysing and documenting the corruption or influence-peddling risks associated with third parties with whom the organisation enters into a relationship. This assessment must be proportionate to the identified risk level and updated according to the rules defined by the organisation.
The third parties to be assessed depend on your corruption risk mapping and your internal policy: strategic suppliers, intermediaries, distributors, agents, partners, or service providers operating in sensitive zones or activities. Our software helps prioritise assessments according to risk level.
This software focuses on third-party integrity assessment within the Sapin 2 framework. Our third-party assessment solution covers a broader, multi-regulatory scope, with contexts such as AML/CFT, NIS2, DORA, CSRD, duty of vigilance, or other frameworks.
Yes. Our software handles multi-entity organisations. Each entity can assess its own third parties, while the compliance department has a consolidated view of the group portfolio.
Yes. Our Sapin 2 third-party assessment software can be deployed on its own. It can also be progressively integrated into our Sapin 2 solution if your organisation wishes to cover other pillars of its anti-corruption programme.
No. Our software helps structure, automate, and document the third-party assessment process. It facilitates traceability and the production of evidence, but the quality of the programme depends on the criteria selected, the data available, the analysis conducted, and the decisions made by the organisation.