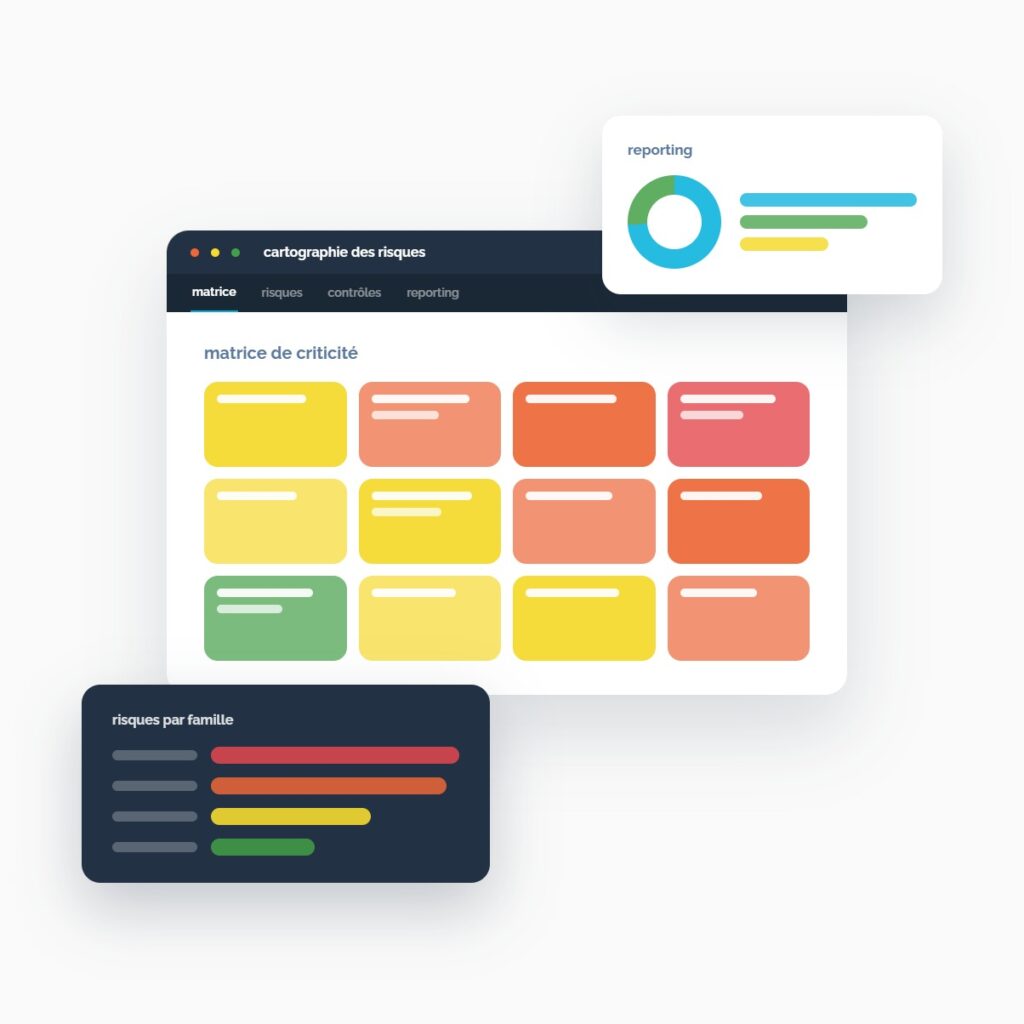
Our risk mapping software helps organizations identify, assess, prioritize, and track their risks within a collaborative, multi-framework interface.
It centralizes risk data, automates collection from contributors, generates dynamic matrices, and delivers dashboards ready for management.
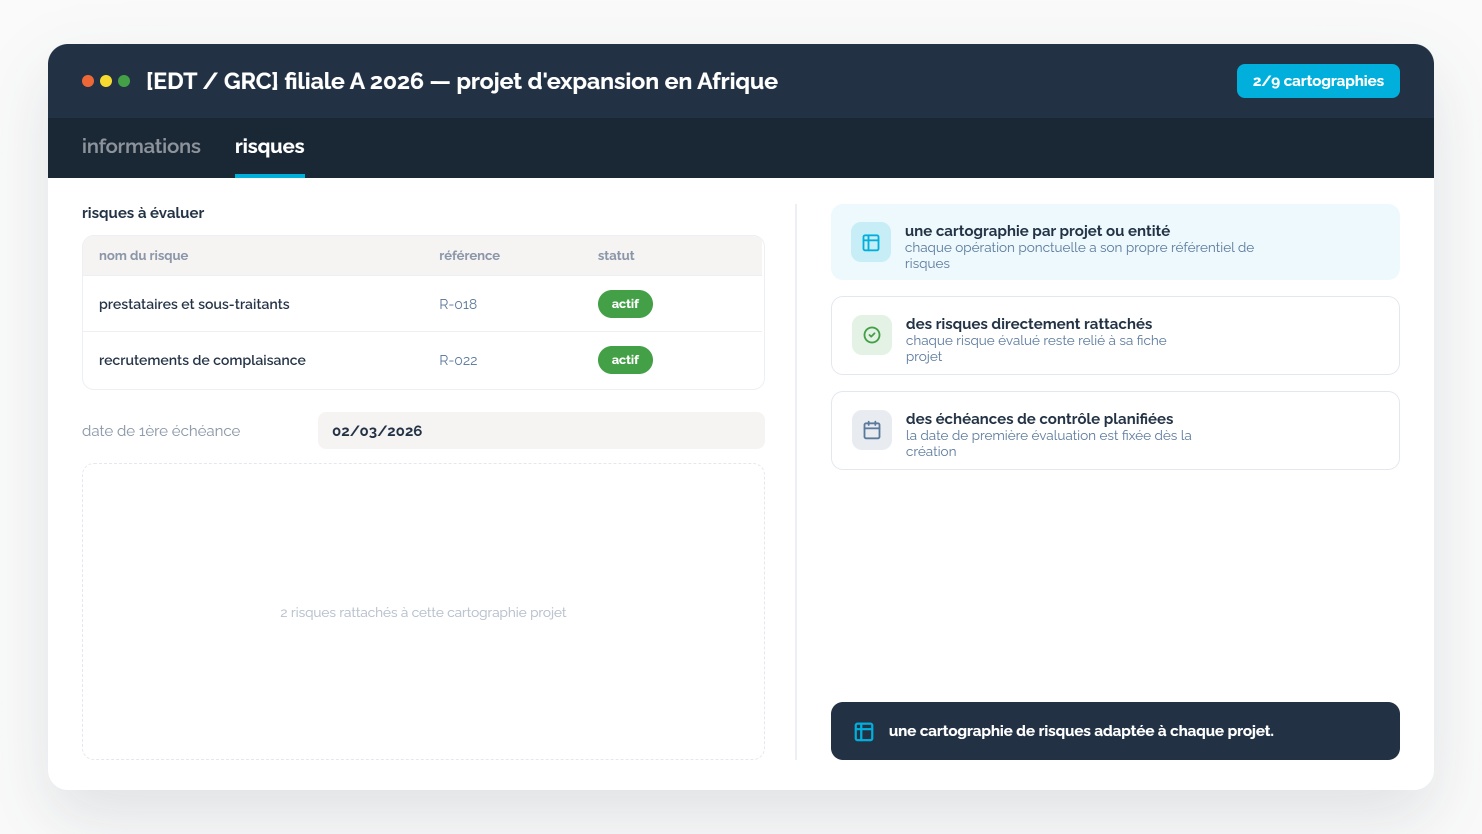
Your entities (subsidiaries, departments, sites) each manage their own risk mapping separately, with no consolidated view, and every campaign starts from scratch.
Each entity enters its risks within its own scope, siloed by default. Data automatically flows into a consolidated cockpit, with built-in validations and automated reminders.
You manage from a consolidated cockpit, for both risks and controls, while each entity retains control over its own scope. No more manual collection by email and time-consuming reminders.
You need to produce your annual risk action plan. The process is manual, and contributors don't always know what to fill in or when to do it.
You launch structured collection campaigns for operational stakeholders. Each contributor only accesses their own scope, and risk scoring goes through a built-in validation workflow, from input by the stakeholder to validation by the risk manager.
The action plan is generated from the data entered, with no manual reconstruction before each deadline. A one-click PDF or Excel export lets you share it with your external stakeholders, regulators, or partners.
You need to manage multiple risk mappings: operational risks, Sapin 2, ESG, cyber, or compliance. Frameworks keep multiplying, and so do the tools.
Your risk mappings coexist on the same platform, each with its own criteria, weightings, entities, and criticality levels.
You get a single, consistent framework. Your teams work within the same tool, with no duplication.

Centralize and qualify your libraries of processes, risks, and controls in a single, structured repository aligned with your organization.
Link the elements together to benefit from a 360° view of your framework.
Not sure where to start? Use our pre-configured libraries to get started quickly.
Prepare and plan your assessment campaigns.
Maintain end-to-end control by tracking their progress

Assess your risks according to your probability and impact weightings.
Define, prioritize, and monitor control measures until they are closed.

Monitor the status of your system at any time using the available dashboards.
Never miss a deadline thanks to automatic notifications that alert the relevant stakeholders at the right time.
Intuitive and fully customizable, it helps you effectively identify and analyze the risks your organization is exposed to.
Manage all your risk mappings, with no limitations, in a single tool: operational risks, corruption risks, cyber risks, ESG risks, AI risks, regulatory risks, and more. Each risk mapping retains its own criteria and weightings.
Risk mapping isn't static: your operational stakeholders collect and update risks, with access configured by scope. It evolves alongside your organization.
Structure your risk mapping by subsidiary, department, business unit, site, or process. You retain both a local view and a consolidated view. Unlimited entities, themes, and risk mappings: your scope can grow without per-unit billing.
Risk mapping works on its own, but it can also integrate with internal control, audit, and action plans within our GRC solution.
Show us your current setup. We’ll present the tool suited to your context, then discuss your project to define the most appropriate support.

The risk mapping software can be used independently. It can also integrate with our GRC solution to connect your risks, controls, audits, and action plans.
Deploy only your risk mapping. You address a specific need, without bringing in an entire programme.
Connect your risk mapping to the 4 modules of the GRC programme for a consolidated view, shared data, and a single file ready for any audit.
Three engagement levels depending on your maturity in risk mapping and the complexity of your organization.
Risk mapping software is a tool that identifies, assesses, prioritizes, and tracks an organization’s risks within a shared framework. It facilitates collection from contributors, risk scoring, matrix generation, and management reporting.
The risk register lists and details all identified risks. Risk mapping represents them visually and ranks them by criticality level, often based on a probability × impact matrix. In our platform, the two coexist natively: the register feeds the risk mapping, which in turn feeds the dashboards.
Yes, our software lets you manage multiple risk mappings within a single tool: Sapin 2, NIS2, DORA, ESG, or internal frameworks, with criteria tailored to each scope.
Our software lets you launch collection campaigns for operational contributors. Users enter their risks directly in the tool, with automatic reminders and a built-in validation workflow.
With the Essential offer, deployment can take under a week thanks to a pre-configured framework. With the Configurable offer, allow around 1 month to adapt the software to your organization. The Made-to-measure offer depends on the scope defined during scoping, but generally requires a minimum of 4 months to deploy.
Yes. The risk mapping software can be deployed on its own. It can then be complemented and linked with the internal control, internal audit, or action plan modules as part of the GRC solution.